Businesses today rarely operate from a single office or even a single country. Employees work remotely, companies use cloud applications, and customers expect services across international markets.
This flexibility creates an important question: Where is business and personal data actually stored, processed, and accessed?
For organizations handling personal information, this is not simply an IT question. GDPR places requirements around how personal data is processed, protected, retained, and transferred. The regulation also emphasizes accountability and appropriate technical and organizational safeguards.
At the same time, some businesses face contractual, industry-specific, or national requirements concerning where data can be stored or processed.
This is where Virtual Desktop Infrastructure (VDI) can become part of a broader data protection strategy.
How Does VDI Help Control Where Business Data Lives?
Traditional endpoint environments can distribute applications and data across laptops, desktops, and other devices. This can make it harder for IT teams to maintain consistent control over sensitive information.
With VDI, the desktop environment is hosted centrally. Users connect to their virtual workspace from an authorized device, while applications and business data can remain within the controlled infrastructure.
This creates a different model:
Instead of moving sensitive data to every employee's device, businesses can bring the employee into a controlled virtual workspace.
For organizations concerned about GDPR and Data Residency, this centralized approach can make it easier to define where virtual desktops and associated data are hosted.
However, businesses must still understand the complete architecture, including backups, storage systems, logs, disaster-recovery environments, and third-party services.
Can VDI Reduce Data Exposure on Employee Devices?
One of the biggest advantages of VDI is the potential for a reduced local data footprint.
If a remote employee loses a laptop, the risk can be lower when sensitive business files are not stored directly on that device. Depending on the VDI architecture and security configuration, the endpoint can primarily provide access to a centrally hosted desktop rather than becoming the main location for business data.
This can be particularly useful for:
- Remote employees
- Contractors
- Hybrid teams
- Customer-service teams
- Financial organizations
- Healthcare businesses
- Companies handling customer PII
Of course, VDI does not eliminate endpoint risk. Devices still require appropriate security controls, authentication, encryption, and management.
Does VDI Automatically Make a Business GDPR Compliant?
No.
This distinction is extremely important.
VDI is a technology that can support GDPR-related security and governance objectives. It does not automatically make an organization GDPR compliant.
GDPR covers areas including lawfulness, purpose limitation, data minimization, storage limitation, integrity and confidentiality, and accountability. Organizations must also address individual rights and appropriate controls around international data transfers.
Therefore, companies should view VDI as one component of their overall compliance framework.
The better question is:
How can VDI help us implement stronger data protection and governance controls?
Data residency generally refers to requirements or organizational policies that specify where data should be stored or processed.
With centrally hosted virtual desktops, organizations can select infrastructure locations that align with their business and regulatory requirements, subject to the capabilities and contractual terms of the chosen provider.
For example, a company operating primarily in Europe may want its virtual desktop infrastructure and related data services hosted within an appropriate European location.
However, simply choosing an EU data center does not resolve every GDPR issue. International access, support operations, backups, subprocessors, and data transfers must also be considered.
The European Commission notes that when personal data is transferred outside the EEA, organizations need an appropriate transfer mechanism or safeguard, such as an adequacy decision or other recognized mechanism.
How Does Centralized Access Help With GDPR Security?
Centralized VDI can give IT administrators greater control over how users access applications and data.
Depending on the platform and configuration, organizations can implement controls such as:
- Multi-factor authentication
- Role-based access
- Session controls
- Encryption
- Restricted copy and paste
- Device restrictions
- Centralized patch management
- User activity logging
Instead of configuring every employee's workstation independently, administrators can establish policies across a centrally managed environment.
This can help businesses create a more consistent security model.
VDI Make GDPR Audits Easier
Another important consideration is visibility.
GDPR's accountability principle means organizations need to be able to demonstrate that they are following appropriate data protection practices.
Centralized infrastructure can simplify the collection and review of information such as login activity, access events, system changes, and user sessions, depending on the platform's logging capabilities.
This does not replace formal compliance documentation, policies, risk assessments, or audits. But better centralized visibility can make it easier for IT and compliance teams to understand what is happening within the environment.
Data Retention and Deletion is Simpler with VDI
GDPR includes a storage limitation principle: personal data should not be kept longer than necessary for its purpose.
Centralizing data can make certain retention processes easier to manage because organizations have fewer scattered endpoints to investigate.
When an employee leaves, for example, administrators can disable access to a centralized workspace without having to rely entirely on the employee returning a device or manually deleting information from multiple systems.
However, organizations still need defined retention schedules and deletion procedures across all relevant systems, including backups and third-party applications.
How Can vDeskWorks Support a GDPR-Focused VDI Strategy?
Businesses evaluating VDI for GDPR can consider platforms such as vDeskWorks when they need a centralized approach to virtual desktops and remote application access.
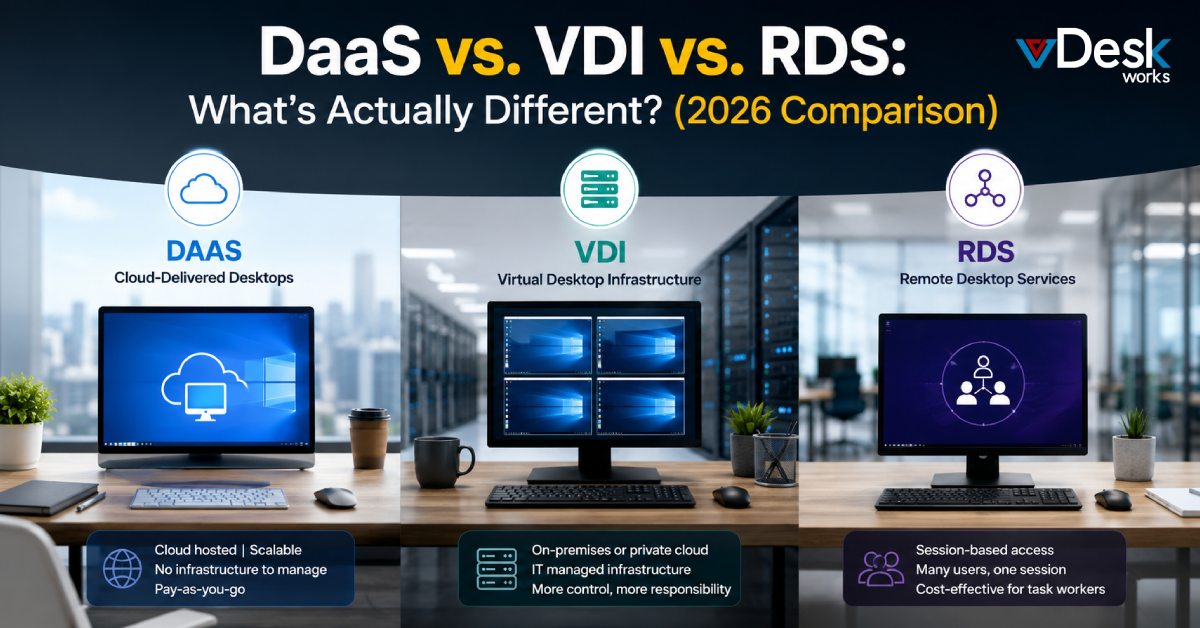
vDeskWorks provides a managed VDI and Desktop as a Service approach designed to centralize desktop environments rather than relying entirely on local employee devices.
Its centralized management model can support organizations looking to control virtual desktop access, manage users, and establish consistent desktop policies.
For businesses with specific residency or sovereignty requirements, deployment architecture becomes especially important. Organizations should evaluate available hosting options, infrastructure location, backup location, access arrangements, and contractual responsibilities before deployment.
In other words, vDeskWorks can be part of a GDPR-focused infrastructure strategy, but the customer's configuration and broader compliance program remain critical.
Final Thoughts
GDPR and Data Residency are becoming increasingly important as businesses operate across borders and support distributed workforces. Organizations need to know not only what data they hold, but also where it is stored, where it is processed, who can access it, and how long it remains available.
VDI can help address some of these challenges by centralizing desktops, reducing reliance on local data storage, strengthening access controls, and providing greater control over infrastructure locations.
For businesses evaluating VDI Compliance, solutions such as vDeskWorks can be considered as part of a broader strategy for centralized and controlled desktop delivery. Book a live demo at www.vdeskworks.com/live-demo-client.
 Emma Carson